Showing posts with label protocol. Show all posts

2016-07-02

Ethereum DAO Hack

The hack makes me think about the reliability of crypto-currency. If we go with the assumption that there is no bug-free software, it is always only a matter of time (hence patching is of utmost importance), then how do we have our faith in bitcoins or any other altcoins?

How can they recover the stolen money? They can't -- at least not without destroying the entire principle of cryptocurrencies

Am very curious to see what this community decides to do now. Hack details.

A synopsis of the hack and the Robin Hood hack.

2016-04-13

Hacking Lottery via Random Num Generator

For several years, Eddie Tipton, the former security director of the US Multi-State Lottery Association, installed software code that allowed him to predict winning numbers on specific days of the year, investigators allege.
Full story!
 

2015-07-03

North America is out of IPv4

Yikkess, you hear about this day will come one day, and here we are. Time to beef up the effort on v6.

2015-06-16

LastPass Compromised

LastPass (a popular password management site) has been compromised. The company announced in their blog. Errata also has a good impact assessment on the topic.

2014-04-10

Hearbleed Bug - Impacting OpenSSL

The Heartbleed Bug is a serious vulnerability in the popular OpenSSL cryptographic software library. This weakness allows stealing the information protected, under normal conditions, by the SSL/TLS encryption used to secure the Internet. 
In short - patch this now! And change your passwords on all the websites that were impacted here.
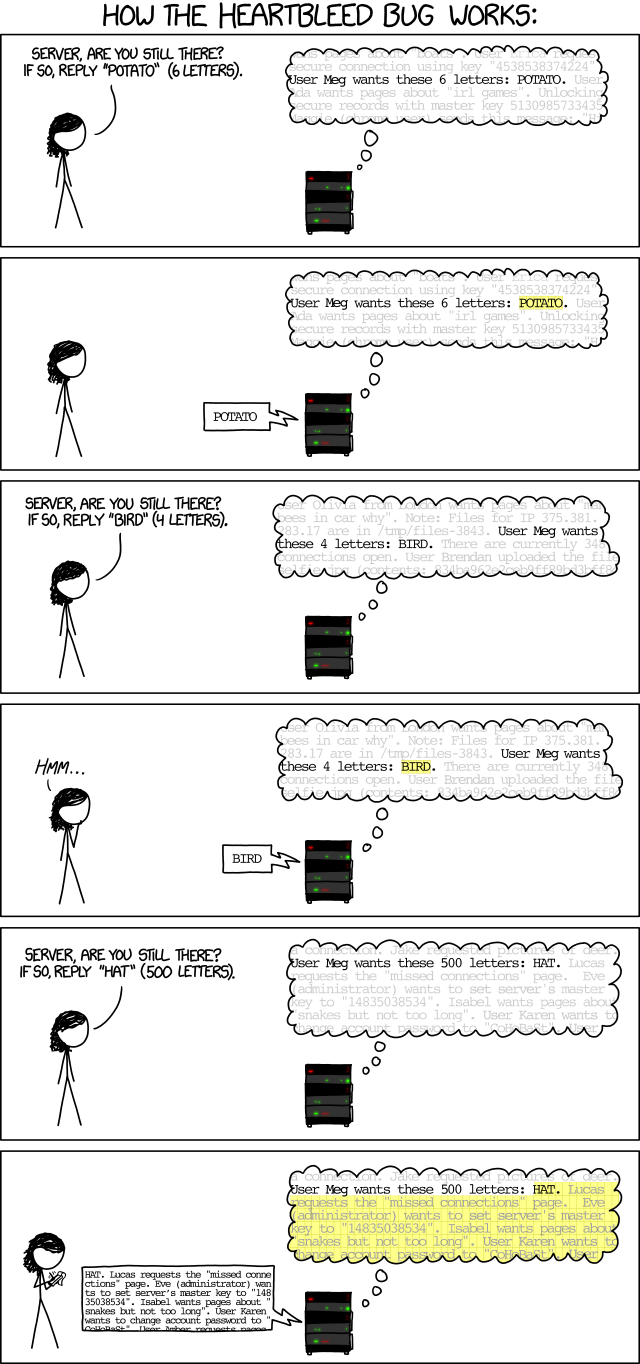
Some explanations here
Tech help here
Home page for the bug
Easy to read explanation
A good FAQ page, management style.

Update 10-May-2014:
300K servers are still vulnerable!

2014-02-15

Now a 400 GBps DDoS attack

Largest in the history, and much bigger than last year's Spamhaus attack [biggest at the time].
Using NTP reflection attack, similar to what was used to attack a few gaming websites recently.

Some more details here. Symantec's tech details

2013-06-01

Two Factor Auth

More companies finally following Google's footsteps and enabling 2FA. Twitter ; Linkedin

Update 09-Aug-2013:
Twitter's state of the art 2FA app

2013-04-25

P2P File Sharing

A much needed solution, for peer-2-peer secure sharing. I can already think of a hundred ways how this service is going to be misused!

2012-08-29

Passwords Cracking - Myths and Realities

It's no news about how insecure passwords are, and why they do not add to any real security. A good post to talk about the common myths around password cracking.

2012-08-05

Is Microsoft Listening on Skype Calls?

Is this rumor is true, then it will mean some serious impact to the privacy of the users (even if some bloggers feel otherwise)

2012-04-13

Finding the New Encryption Standard

04-Oct-2011:
NIST began a public contest in 2008 to find a hash function to serve as the SHA-3 standard. Here is a status update on this project. One of the algos will be chosen in 2012.


13-Apr-2012:
Another update on the shortlisted candidates 

2011-10-23

2011-09-21

SSL vs TLS

In case a better understanding is required around the difference in these two protocols.
[Not a big difference, basically TLS is a successor to SSL]

Update 13-Apr-13:
New version of SSH introduced.

2011-09-06

Attack on DNS - NetNames

This is pretty upsetting... A compromised DNS, would render all the security controls of a website useless. The website will be totally at the mercy of the attacker